Security
Business VPN: secure access to company resources anywhere
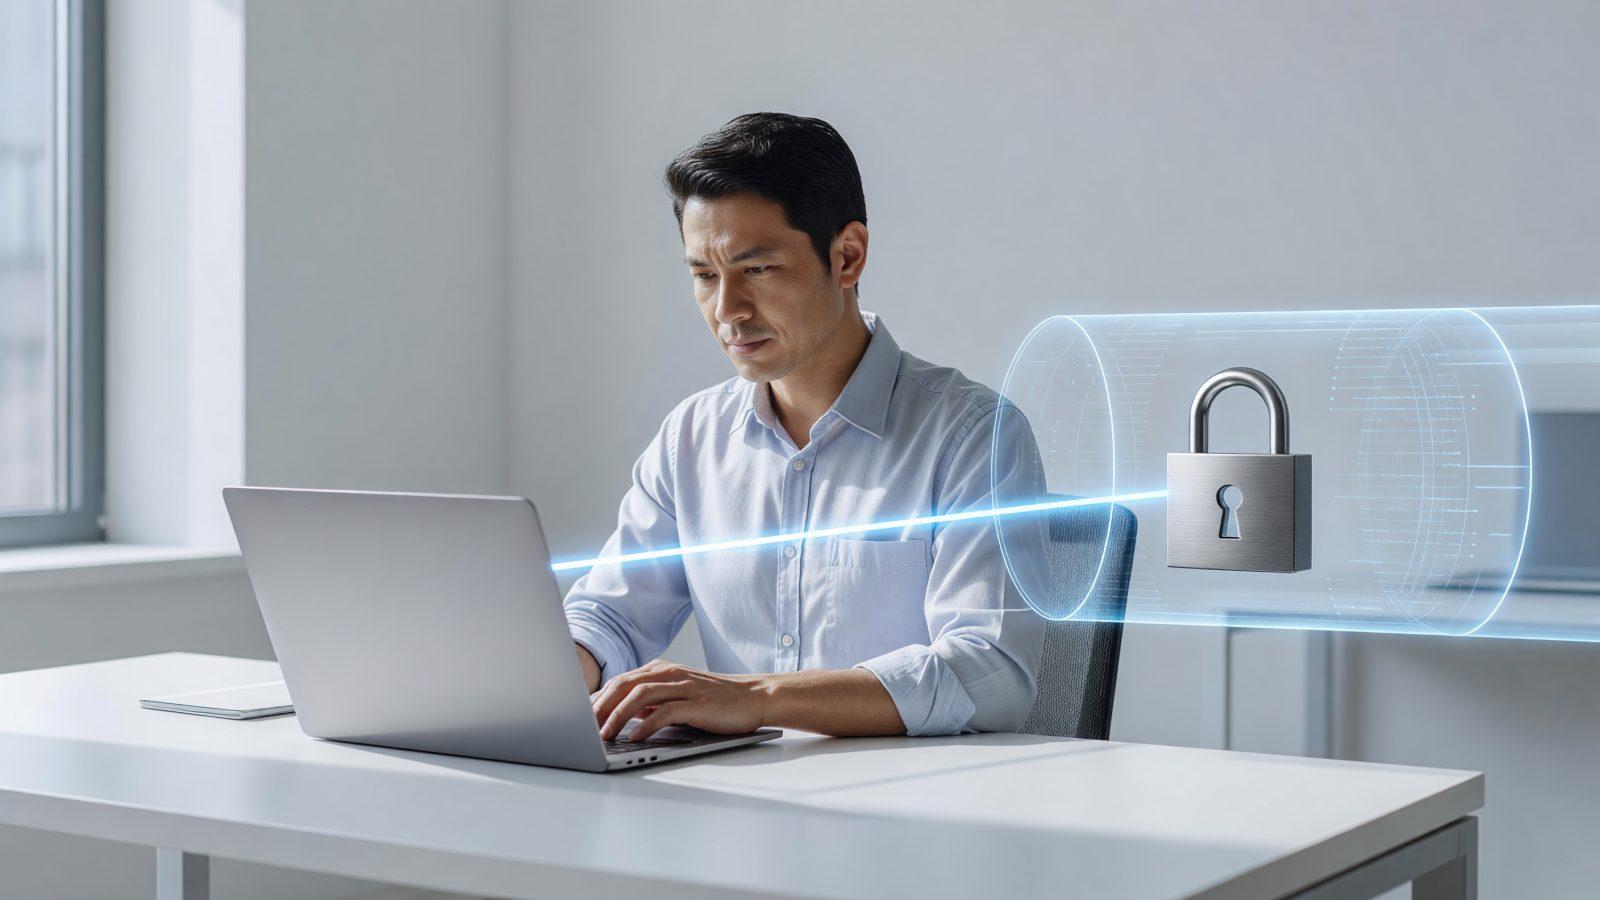
A business VPN creates an encrypted tunnel between an employee computer and the company network, so they can work as if physically at the office, wherever they actually are. It is used for access to internal files, accounting software or servers that are not published directly on the internet. Set up correctly, with two-factor authentication and access limited by network zone, it is one of the most effective security measures for remote work.
What a business VPN is actually for
A business VPN has one job: letting people connect remotely to resources that, for security reasons, are not exposed publicly on the internet — a file server, a management application, a database. Without a VPN, the only alternative would be publishing those resources directly online, exposing them to anyone scanning the network. With a VPN, the employee connects through an encrypted tunnel and the resource stays invisible from the outside.
What you actually expose matters as much as how people connect. Publish directly on the internet only what genuinely needs to be reachable from outside — a website or a client portal, for instance — and keep everything else (file servers, internal applications, databases) reachable only through the VPN tunnel, never directly on the internet, no matter how convenient that might seem in the short term.
How it differs from consumer VPNs
A consumer VPN (used to change your apparent location or watch region-locked content) solves a completely different problem: hiding your traffic on the public internet. A business VPN does the opposite — it connects you into a private network rather than hiding you from one. The two get confused often, but using a consumer VPN app to reach company resources gives no control over who connects, what they can access, or how long a session stays open.
Site-to-site vs. client-to-site
- Site-to-site — permanently links two networks, for example headquarters and a branch office, so they behave as one local network. There is no manual connecting; the tunnel stays up.
- Client-to-site — an individual employee connects from a laptop or phone, from home or on the road, through a VPN app. It is turned on and off as needed.
A single-location company with employees working from home mainly needs client-to-site VPN. A company with several offices or warehouses also needs site-to-site links between them.
Why a VPN alone is not enough
A VPN without two-factor authentication (2FA) means that anyone who obtains a password — stolen, guessed or reused from another site — can walk straight into the company network. 2FA adds a second verification step, usually a code on a phone, which stops exactly this scenario even if the password has been compromised.
Just as important is what happens after the connection is made. A poorly configured VPN grants access to the entire network, as if the employee were sitting at any desk in the building. Segmentation (separate VLANs for accounting, production, guests) limits access to only what a given role actually needs. A marketing employee has no reason to reach the payroll server, even connected through the VPN.
Common mistakes to avoid
- A shared account for several employees — makes it impossible to tell who connected and when, during an audit or an incident.
- Full network access after connecting — without segmentation, one compromised password endangers the entire infrastructure.
- Accounts left active after an employee leaves — if offboarding does not include immediately disabling VPN access, a former employee keeps an open door for months.
Modern alternatives: per-application access, not full-network access
Newer remote access models (zero-trust or application-level access) no longer open a tunnel to the whole network. Instead, they grant access application by application, checked on every request. They are more complex to set up than a classic VPN, but they drastically reduce what is exposed if an account is compromised. For many small companies, though, a well-configured VPN with 2FA and segmentation remains the right balance of cost and security.
The practical difference shows up most for companies with many external collaborators or employees working exclusively from a phone — there, per-application access shrinks the attack surface without complicating daily work. For a company with a single office and a stable team, moving to such a model rarely pays off right away.
How to start
Setting up a business VPN correctly starts with VLAN segmentation of the network and a security audit that shows exactly what needs protecting. Contact us for a setup matched to your company size.