Security
Firewall and network segmentation: your first line of defense
The router your internet provider hands you for free was not built to defend a business — it was built to deliver a connection at minimum cost. A business-grade firewall, combined with a network correctly segmented into VLANs, is the real first barrier between the internet and your company's computers, servers and cameras. Without it, a single infected workstation can reach everything else on the network within minutes. This is a separate layer from antivirus or backup — it is about what happens before a problem gets the chance to spread.
Business firewall vs. your ISP router
A basic router does NAT and little else — it lets outbound traffic pass unchecked and offers minimal inbound rules. A business firewall inspects traffic in both directions, applies separate rules per network zone, and can actively block a suspicious connection instead of just passing it along. The difference shows most when something goes wrong: a basic router will not tell you what happened, a business firewall keeps a log. For a company with 15-20 computers and a couple of servers, the cost of a dedicated firewall is usually well below the cost of one hour of downtime from an undetected incident.
Inbound and outbound rules
Many companies only think about inbound rules — what can reach the internal network from the internet. Outbound rules matter just as much: what an internal workstation is allowed to contact outside. An infected computer usually talks back to a command server somewhere on the internet — if outbound rules are strict, that communication gets blocked even after the infection is already in. In practice, many companies lock down inbound rules tightly but leave outbound traffic completely open, which cancels out much of that protection.
Why VLAN segmentation matters
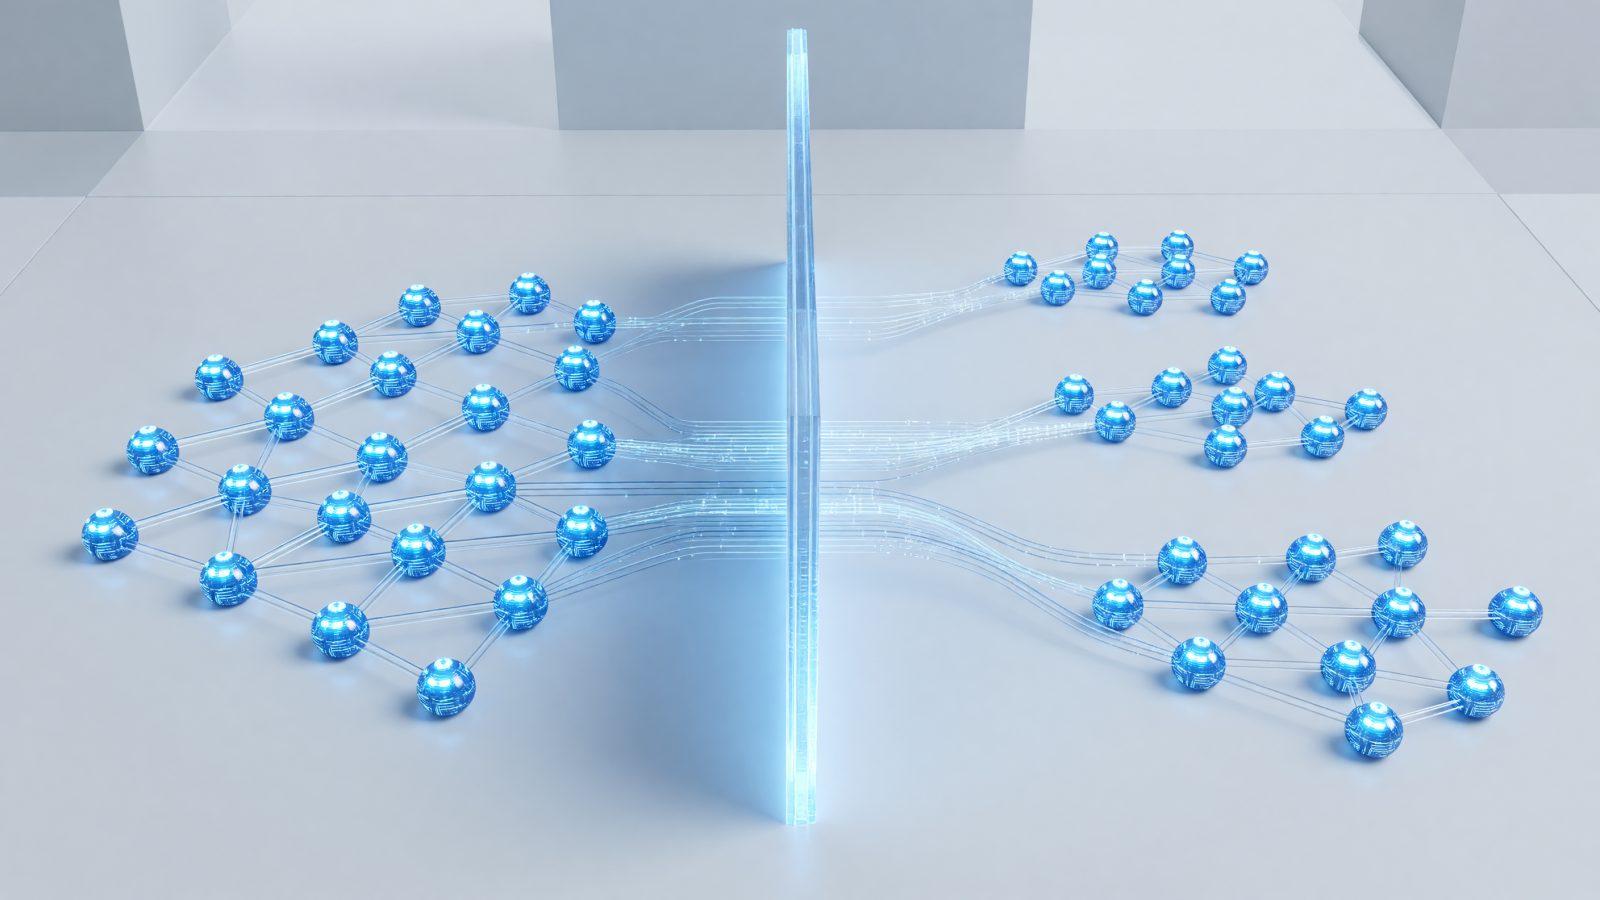
Segmentation splits one physical network into separate logical networks that only talk to each other through explicit firewall rules. In a typical company, it makes sense to separate at least:
- The office network — employee computers, with access to work applications.
- The guest network — visitor wifi, with no access to internal resources.
- The camera network — surveillance equipment, isolated from the rest, since it is a frequent target for automated attacks.
- The production equipment network — connected machinery or industrial systems, which rarely receive security updates.
Each zone only talks to what it strictly needs — surveillance cameras, for instance, have no real reason to reach the internet or the accounting folders.
Example — how an infection spreads on a flat network
On a "flat" network with no segmentation, every device can see every other device. A laptop infected through a phishing email automatically scans the local network, finds a vulnerable workstation, then a server, then the cameras connected to the same network — all within a few hours, with no human involvement. With segmentation, the same infection stays contained in the office zone: the firewall will not let traffic through to cameras or production equipment unless it is explicitly allowed. The difference between an hour of downtime in one department and a full company shutdown comes down to exactly this separation.
What you log, and who actually watches it
A business firewall generates logs of blocked connections, triggered rules and unusual traffic. The real problem at small companies is not a lack of logs, it is that nobody looks at them — they pile up unread until an incident happens. It makes sense either to have someone in-house check the important alerts regularly, or to have an outside IT provider run continuous monitoring and actively flag anything unusual, rather than just keeping logs "just in case". Responding to a real alert within a few hours is the difference between a minor incident and serious damage.
Signs your network needs a better architecture
- Every device, from laptops to cameras, sits on the same network with no separation at all;
- The guest network uses the same SSID or address range as the internal one;
- Nobody knows exactly which firewall rules are active or who configured them;
- The company grew from a handful to dozens of employees, but the network never changed since day one.
How to start
Assessing your current architecture starts with a properly configured firewall, followed by VLAN segmentation for critical zones and, for remote access, a secure VPN. Contact us for an assessment of your current network.